Trusted IT Support For Regulated Finance Teams
Managed IT Support For Financial Services
AIS Technology provides IT support for financial services firms in London and Essex, including independent financial advisers, accountancy practices, other FCA-regulated firms and the finance teams inside larger businesses. Client data is sensitive, deadlines are fixed, and the FCA expects a firm to show that its IT is under control.
Every client gets a one-hour response SLA and a service desk that answers 24 hours a day. For regulated firms, the optional compliance portal keeps the evidence an auditor, the FCA or a client will ask to see.
Financial services IT at a glance
What does IT support for a financial services firm include?
AIS Technology provides IT support to financial services firms, accountants and accounting practices across Essex and London. The core is the same managed IT plan every client gets, at £35 per device per month with Microsoft 365 licensing bought separately, with a one-hour response SLA and a 24/7 service desk, because a finance team that loses email, files or remote access loses billable time immediately.
Round-the-clock endpoint detection and response, identity and account protection and a dedicated Security Operations Centre are already in that plan. What a regulated firm adds on top is the evidence layer: the compliance portal, at £100 per organisation per month, covers FCA and GDPR support, advanced reporting and the client security questionnaires that come with financial work. Every managed client is baselined to the Cyber Essentials standard as a matter of course.
| What it covers | Why a finance firm needs it | Cost |
|---|---|---|
| Helpdesk and one-hour SLA | Downtime in a finance team is billable time lost, and deadlines are fixed | Included, £35 per device per month |
| Proactive monitoring and patching | Unpatched systems are the most common finding in a supplier audit | Included |
| Daily Microsoft 365 backups | Client records have to be restorable after a loss or an attack | Included |
| Cyber Essentials baseline | The minimum standard clients and insurers ask to see | Included; IASME fee from £320 + VAT on top |
| 24/7 identity and endpoint threat detection | Identity is the primary attack surface in financial services | Included |
| FCA and GDPR reporting support | Regulators expect a control set you can demonstrate, not describe | Compliance portal, £100 per organisation per month |
| Client security questionnaires | Financial clients send them, and they need real evidence behind them | Compliance portal |
| Specialist cover | Accountants and accounting firms, including practice software | Included |
Prices exclude VAT and run on a three-month rolling contract. Microsoft 365 licensing is required separately.
Support That Helps Financial Teams Work Without Disruption
When a finance team loses access to email, files, line of business apps, or remote access, the impact is immediate. Work slows, client service suffers, and risk rises.
Support is built around responsive helpdesk support, proactive monitoring, and clear ownership of issues. Many problems are resolved remotely, while onsite support is available when hardware, network faults, or office changes need hands on help.
If you want to see what is included and how the plans are structured, IT Packages sets out the plan features and pricing notes.
What We Do For You:
Fast Response: We answer the phone when you call. No endless hold music.
London & Essex Based Team: We are local and can be on site when you need us.
Proactive Fixes: We find glitches before they stop your work.
Finance Security Background: Chris Dunham, our founder, secured systems for UK financial institutions and government bodies, including the Home Office, before founding AIS Technology.
FCA outsourcing rules
What does the FCA expect from a regulated firm's IT provider?
The FCA treats a managed IT provider as an outsourcing arrangement. Its guidance on cloud and IT outsourcing, FG16/5, says that where a third party delivers services on behalf of a regulated firm, that is outsourcing, and SYSC 8 of the FCA Handbook sets out what the firm has to do about it. The firm remains fully responsible for its regulatory obligations and cannot pass that responsibility to the provider.
For MiFID investment firms the conditions in SYSC 8.1.8R are binding rules. For most other small firms, including advisers who pass client orders to platforms, mortgage brokers and insurance intermediaries, they apply as guidance, in proportion to the size of the firm. Either way, the FCA, auditors and clients judge an IT arrangement against the same list, and AIS Technology's view is that a regulated firm should be able to show the evidence for every line of it.
| FCA expectation | What it means for your IT | Evidence to keep on file |
|---|---|---|
| A capable provider (SYSC 8.1.8R(1)) | Enough engineers to cover your working hours, and sound security of its own | The size of the support team, the out-of-hours arrangements and the provider's own security certificates |
| Performance you can measure (SYSC 8.1.8R(2)) | Service levels written into the contract and reported against | Response times in writing, and regular reports on support tickets, patching, backups and security alerts |
| The provider controls its own risks (SYSC 8.1.8R(3)) | Engineers' access to your systems is protected | How administrator accounts are secured, whether multi-factor authentication is enforced, and who can reach your data |
| Notice of developments (SYSC 8.1.8R(6)) | Prompt notice of security incidents, outages and changes to the service | An agreed notification time for incidents, and notice before a change of subcontractor or data location |
| Access to data (SYSC 8.1.8R(9)) | Your firm, its auditors and the FCA can reach your data, logs and records | An access clause that sets no limit on how many requests you, your auditor or the FCA can make (FG16/5) |
| Client confidentiality (SYSC 8.1.8R(10)) | Client data is handled under proper data protection terms | A UK GDPR data processing agreement and a record of where your data is stored |
| Disaster recovery (SYSC 8.1.8R(11)) | A recovery plan, and backup facilities that are tested periodically | The backup schedule, the recovery plan and a record of the last restore test |
| Subcontractors only with consent (SYSC 8.1.9R) | You know which other companies handle your systems and data | A current list of every company in the supply chain, including Microsoft and the backup service |
| The ability to leave (SYSC 8.1.8R(7) and (12)) | You can change provider without harming clients | Termination rights, a short exit plan, and confirmation that your firm owns its Microsoft 365 tenant and domain names |
Summarised from SYSC 8.1 of the FCA Handbook and FG16/5, as they stood in November 2026. The wording in the first column is ours. Whether a condition binds your firm as a rule or applies as guidance depends on your permissions, which your compliance adviser can confirm.
FCA incident reporting
New incident reporting rules apply from 18 March 2027
In March 2026 the FCA published policy statement PS26/2. From 18 March 2027, every firm with a Part 4A permission, including core and limited scope SM&CR firms, must report an operational incident that crosses the FCA's thresholds. Around 90% of regulated firms will use a single short form. The FCA expects the first report as soon as practicable and at the latest within 24 hours of the firm deciding that a threshold is met (SUP 15.18.7G).
How quickly your IT provider tells you about an incident decides how much of those 24 hours you have left. The FCA said in July 2026 that 27% of the incidents firms reported in 2025 were attributed to a third party, and that 37% of those were cyber related. A provider that takes two days to mention an intrusion its monitoring found makes the deadline impossible to meet.
The FCA's separate operational resilience rules in SYSC 15A, with their important business services and impact tolerances, do not apply to core or limited scope SM&CR firms. Incident reporting does.
Sources: PS26/2, FCA, March 2026; Strengthening resilience across an increasingly interconnected financial system, FCA, 28 July 2026; SYSC 15A.1, FCA Handbook.
Audit evidence
The evidence an auditor, the FCA or a client will ask to see
A compliance review, an FCA enquiry and a client's security questionnaire ask for much the same proof: that devices are protected, that access is controlled, that data can be recovered and that someone is watching for attacks. The firm has to produce it whether or not its IT provider helps.
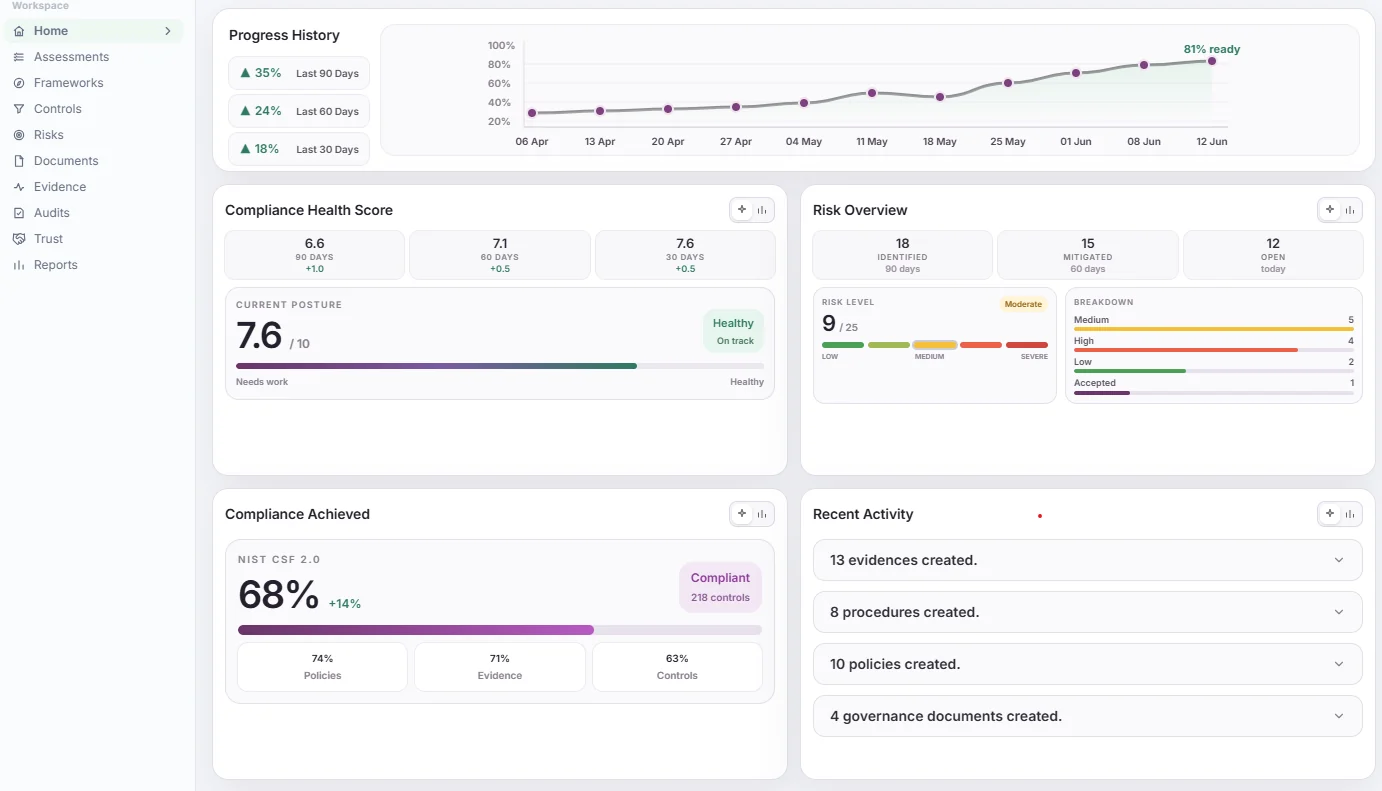
With AIS, most of that proof comes from the plan itself. The compliance portal then keeps it in one live dashboard, with each policy, procedure and piece of evidence stored against the control it proves, so a question from an auditor or a client is answered from current records.
Click to expand
| Evidence | Where it comes from | Included in |
|---|---|---|
| Cyber Essentials baseline | Every managed client is set up to the Cyber Essentials standard | Plan (IASME certification fee from £320 + VAT on top) |
| Security monitoring and alerts | 24/7 endpoint detection and response, identity and account protection, and the Security Operations Centre | Plan |
| Patching and device health | Proactive monitoring and patching of devices, servers and cloud services | Plan |
| Recoverable client data | Microsoft 365 backup and recovery | Plan |
| Joiners and leavers | Employee onboarding, offboarding and device provisioning | Plan |
| Policies, procedures and control evidence | Each document stored against the control it proves | Compliance portal |
| Risk register | Severity breakdown and mitigation tracking | Compliance portal |
| Progress against a framework | A compliance health score and NIST CSF 2.0 progress tracking | Compliance portal |
| Client security questionnaires | Completed questionnaires with their supporting evidence | Compliance portal |
| Staff mobile phones | Mobile device security for iPhone and Android | Compliance portal |
The plan is £35 per device per month and the compliance portal £100 per organisation per month, both excluding VAT and on the same three-month rolling contract. Microsoft 365 licensing is bought separately.
Managed IT Services for Finance Teams with Predictable Performance Requirements
Managed IT services for finance are about removing the daily friction that slows teams down. AIS monitors your devices, servers, and cloud services, then fixes issues before they become outages. Patch management, security updates, and routine maintenance are handled as part of the service, so you are not relying on someone remembering to “get round to it”.
Support is backed by a dedicated helpdesk, with same day engineer dispatch available when onsite help is needed. You also benefit from the wider vendor relationships AIS holds with Microsoft, Dell, and Cisco.
Support Designed Specifically For Accountants And Accountancy Firms
Accountants and accounting firms often run a mix of legacy software, cloud platforms, and client portals, all while working to immovable deadlines. We provide IT support for accountants that keeps core workflows steady during VAT periods, year end, payroll runs, and audit season.
That includes device management, secure remote access, email and collaboration support, and practical troubleshooting that gets people back to work quickly. If your firm is growing and adding staff, AIS can standardise laptop builds, permissions, and onboarding so new starters are productive without creating security gaps.
Improving Efficiency With Microsoft 365 Support For Financial Services
Many financial organisations rely on Microsoft 365 as their central working hub. Issues with Outlook, Excel, shared files or Dynamics 365 can slow entire teams. AIS provides specialist help that keeps these tools running smoothly. Common Areas Where Financial Teams Need Help:
- Outlook and mailbox access issues
- Permission errors for shared folders
- Problems with multiple users in Office applications
- Support for Dynamics 365 finance and operations
- Guidance for secure Microsoft cloud setups
Secure Cloud Support Through Azure For Financial Services
Cloud systems bring flexibility but also greater responsibility. AIS helps financial organisations use Azure safely, ensuring that sensitive information stays under full control while staff can still access what they need. What Azure Support Includes:
- Access management for cloud systems
- Monitoring for unusual data activity
- Secure storage for financial records
- Setups that support cloud financial management
- Support for Microsoft Azure financial tools
Common questions about IT support for financial services
What does IT support for a financial services firm include?
AIS Technology's plan covers a service desk that answers 24 hours a day with a one-hour response SLA, proactive monitoring and patching, onboarding and offboarding, Microsoft 365 backup and recovery, 24/7 endpoint detection and response, identity and account protection and a dedicated Security Operations Centre. It costs £35 per device per month, excluding VAT, on a three-month rolling contract, and Microsoft 365 licensing is bought separately. Most regulated firms add the compliance portal, at £100 per organisation per month, for FCA and GDPR support and their audit evidence.
Does the FCA treat our IT provider as an outsourcing arrangement?
In most cases, yes. The FCA's guidance on cloud and IT outsourcing, FG16/5, says that where a third party delivers services on behalf of a regulated firm, the FCA considers that to be outsourcing. If a failure at the provider would materially impair your compliance or your service to clients, the function is critical or important under SYSC 8.1.4R, and the conditions in SYSC 8.1.8R are the standard the arrangement is judged against. Your firm stays fully responsible for its regulatory obligations whichever provider it uses.
What changes for FCA-regulated firms on 18 March 2027?
The incident reporting rules in the FCA's policy statement PS26/2 come into force. Every firm with a Part 4A permission, including core and limited scope SM&CR firms, must report an operational incident that meets the FCA's thresholds. The FCA expects the first report as soon as practicable and at the latest within 24 hours of the firm deciding a threshold is met. Most firms will use a single short form. Your IT provider needs to tell you about a serious incident quickly enough for you to make that report.
Do the FCA's operational resilience rules in SYSC 15A apply to my firm?
Not if you are a core or limited scope SM&CR firm, which covers most small advice firms, brokers and other small regulated firms. SYSC 15A applies to enhanced scope SM&CR firms, banks, building societies, designated investment firms, Solvency II firms, payment and e-money institutions and a few others. The outsourcing requirements in SYSC 8, the systems and controls rules in SYSC 4 and the Principles apply to small firms regardless, and so will incident reporting from 18 March 2027.
Does our IT provider need ISO 27001 certification?
The FCA does not require it. FG16/5 says that assurance from an international standard is useful when you check a provider, but is unlikely to be sufficient on its own for critical or important functions. A certificate describes how the provider runs itself, not how your own systems are set up. Every AIS managed client is set up to the Cyber Essentials standard, and AIS runs ISO 27001 readiness programmes for firms whose own clients ask for it.
What evidence can we show an auditor or the FCA?
The compliance portal keeps your policies, procedures and evidence stored against the controls they prove, with a risk register, a compliance health score and reporting you can share. Alongside it you have the Cyber Essentials baseline, the 24/7 security monitoring from the Security Operations Centre and Microsoft 365 backup and recovery. Completed client security questionnaires and their supporting evidence are part of the portal too.
How is IT support for accountants different from general business support?
Accountancy practices work to fixed dates such as VAT quarters, the 31 January self assessment deadline and client year ends, and they hold financial records that have to stay confidential. Support for a practice puts the practice and accounting software, Excel and secure file sharing with clients first, and response times matter most in the weeks before a deadline. Third-party application support is included in the AIS plan, so the practice software is covered along with Microsoft 365.
Can AIS support Microsoft Dynamics 365 Finance and Operations?
Yes. AIS supports firms using Dynamics 365 Finance and Operations with user access, performance and configuration problems, and with how it works alongside Outlook, Excel and the rest of Microsoft 365.
Can you support office and remote staff?
Yes. Most problems are fixed remotely, and the plan covers secure remote access, device monitoring and Microsoft 365 sign-in problems wherever staff work. Engineers can be on site in Essex and London when hardware, network faults or an office move need someone in the room.
What size of financial services firm does AIS support?
Small and medium firms across Essex and London, including independent financial advisers, accountancy practices, other FCA-regulated firms and finance departments inside larger businesses. AIS looks after more than 600 users in total. The plan is priced per device, so the cost moves with the size of the firm.
Still weighing up providers? Read our guide on how to choose an IT support partner for financial services.
Speak With AIS About Managed IT Support for Financial Services
Financial organisations deserve support that is consistent, informed and patient. If your team would benefit from steady, knowledgeable IT support, AIS is ready to help.
AIS Technology, Woodland Place, Hurricane Way, Wickford, SS11 8YB